Payment Security Solution
DCVV Solution
Background
A card-not-present transaction (CNP) is a payment card transaction in which the cardholder does not or cannot physically present the card for the merchant's visual examination when the order is placed and the payment is processed. It is most commonly used for payments made over the Internet.
Card-not-present transactions are a major route for credit card fraud, because it is difficult for a merchant to verify that the actual cardholder is indeed authorizing a purchase.
The card security code (CVV in most cases) system was set up to reduce CNP fraud, but it is still insecure to rely on a static 3- (or 4-) digit number to protect the cardholder's property.
In this case, a constantly-changing CVV code solution greatly improves protection against CNP fraud.
Solution
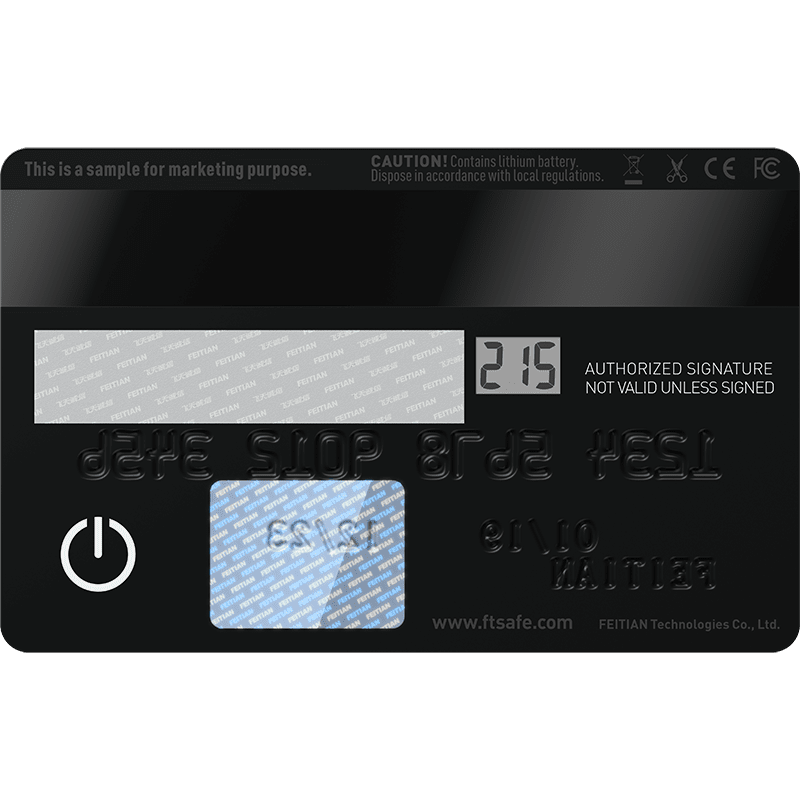
The DCVV (or DCSC) card is a credit card with a screen that displays a time-based one-time password. Unlike normal OTP tokens/cards that use the OATH standard, the DCVV follows the VISA/MasterCard/UnionPay Dynamic CVV requirements.
Bringing a DCVV solution to market requires 3 key parts:
1) Physical card
The physical DCVV card is a security device in the standard ID-1 card form, which contains:
A smart card chip for downloading the financial applets;
Complete card surface printing (without embossed fonts);
A hologram and signature panel;
A flexible circuit board with a battery and screen to display the DCVV value;
A cold lamination process for the manufacturing stage.
FEITIAN handles the entire manufacturing process and provides the physical card.
2) Personalization
Normally, all credit cards require personalization before final issuance. At this stage, the bank chooses a personalization provider to download the sensitive data into the card.
For a standard credit card, this process downloads the credit card applet with the cardholder information into the card and applies the embossing. For a DCVV card, it also requires downloading the dynamic CVV information into the card, including the secret key and the time.
Because the card uses a special communication protocol, FEITIAN provides the devices and guidance to help the personalization provider interact with the card.
3) Authentication System
A back-end server is required for DCVV authentication — normally an extra authentication step compared to a standard credit card transaction.
When the bank server receives the payment request, it sends the related information to the authentication server and waits for the reply. The authentication system is a modified FEITIAN OTP server that supports the DCVV algorithm.
FEITIAN helps the bank deploy the authentication system and provides guidance for any customization of the bank's existing system.
 京公网安备11010802041806号